Security strategy is mostly communication
Security strategy only moves the business when risk is translated into plain language, business impact, tradeoffs, and action.
That may sound surprising coming from someone who works in security and privacy.
But the longer I do this job, the more I realize that the technical part is often the (quote-unquote) easy part. The real challenge is making risk understandable to the people who have to act on it.
Quick Answer
Security strategy is mostly communication because a strategy only matters when people with authority understand the risk, the tradeoff, and the next action. The work is not finished when the security team has the right answer; it is finished when the business can use that answer to make a decision.
- Security strategy is mostly communication because strategy only works when people understand the risk and the decision in front of them.
- It matters because strong controls, roadmaps, and frameworks still fail when executives and product teams cannot translate them into action.
- The practical move is to explain business impact, tradeoffs, and next steps in language the audience can use.
That is why security strategy is mostly communication. The strategy only matters if the people with authority can understand the risk, the tradeoff and the next move.
I’ve seen security teams produce very solid strategies: great frameworks, clear controls, well-structured roadmaps. And yet nothing moves. Not because the strategy is wrong, but because it isn’t translated for the audience.
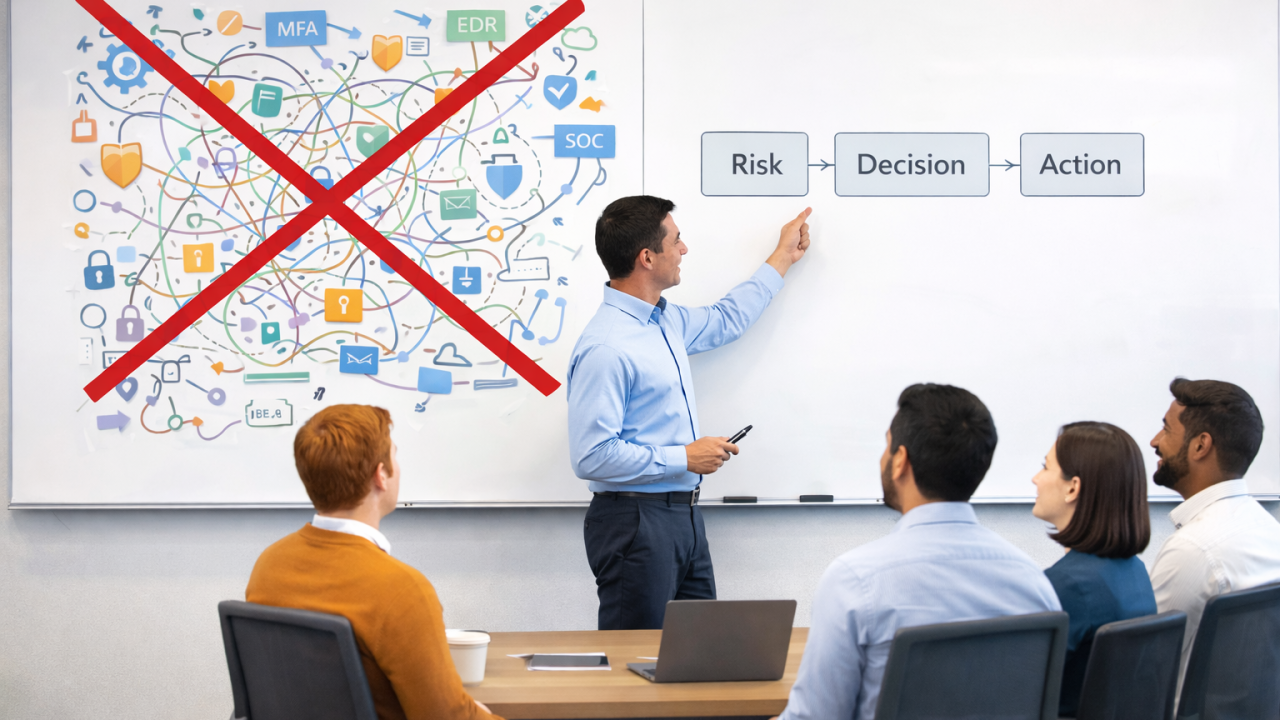
A CTO doesn’t want a list of controls.
A product leader doesn’t want a lecture about frameworks.
An executive team doesn’t want a heatmap with 20 colors.
What they want to understand is simple: what could happen, how it affects the business and what we should do next.
10 years ago, perception bothered me. Now, I embrace optics. Over time, I’ve learned to spend as much effort on the translation as on the strategy itself.
A few practices that helped:
- Start with business impact, not vulnerabilities.
- Use plain language. If I need 5 acronyms to explain something, I probably haven't simplified it enough.
- Show tradeoffs instead of perfect solutions. Executives make decisions, not diagrams.
- Keep security updates short and focused on action.
When the message is clear, something interesting happens: conversations improve. Product teams engage earlier. Leadership decisions get faster.
The strategy didn’t change. Only the way it was communicated did.
That is the hidden work of security leadership: turn accurate technical judgment into shared operating language before the organization has to make the call under pressure.
And on a Friday, that’s a good reminder: the best security programs aren’t just well designed. They are also well explained.